Recognises applications, not ports200+
Almost everything is HTTPS on 443, so a port-based rule can only permit or deny all of it.
Zedmos NGFW
Zedmos NGFW is a complete firewall: our own FreeBSD-based operating system, an inline inspection engine attached straight to the interfaces, and a policy model that decides once per session. Installed from an image onto hardware you choose.
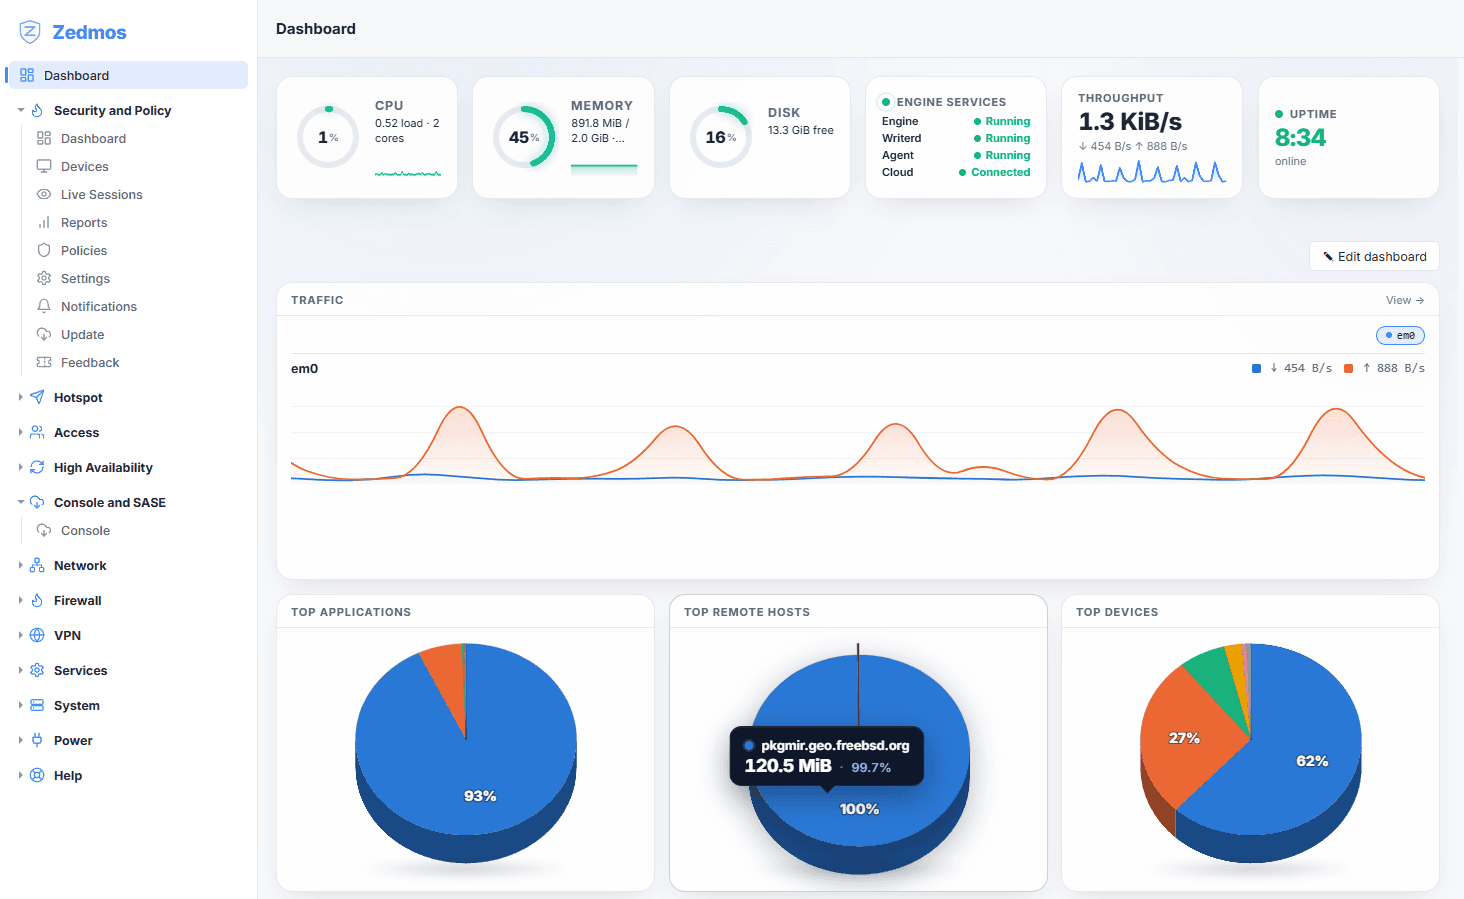
The complete firewall, with the same engine and the same policy model as the plugin — on an operating system we maintain, installed from one image.
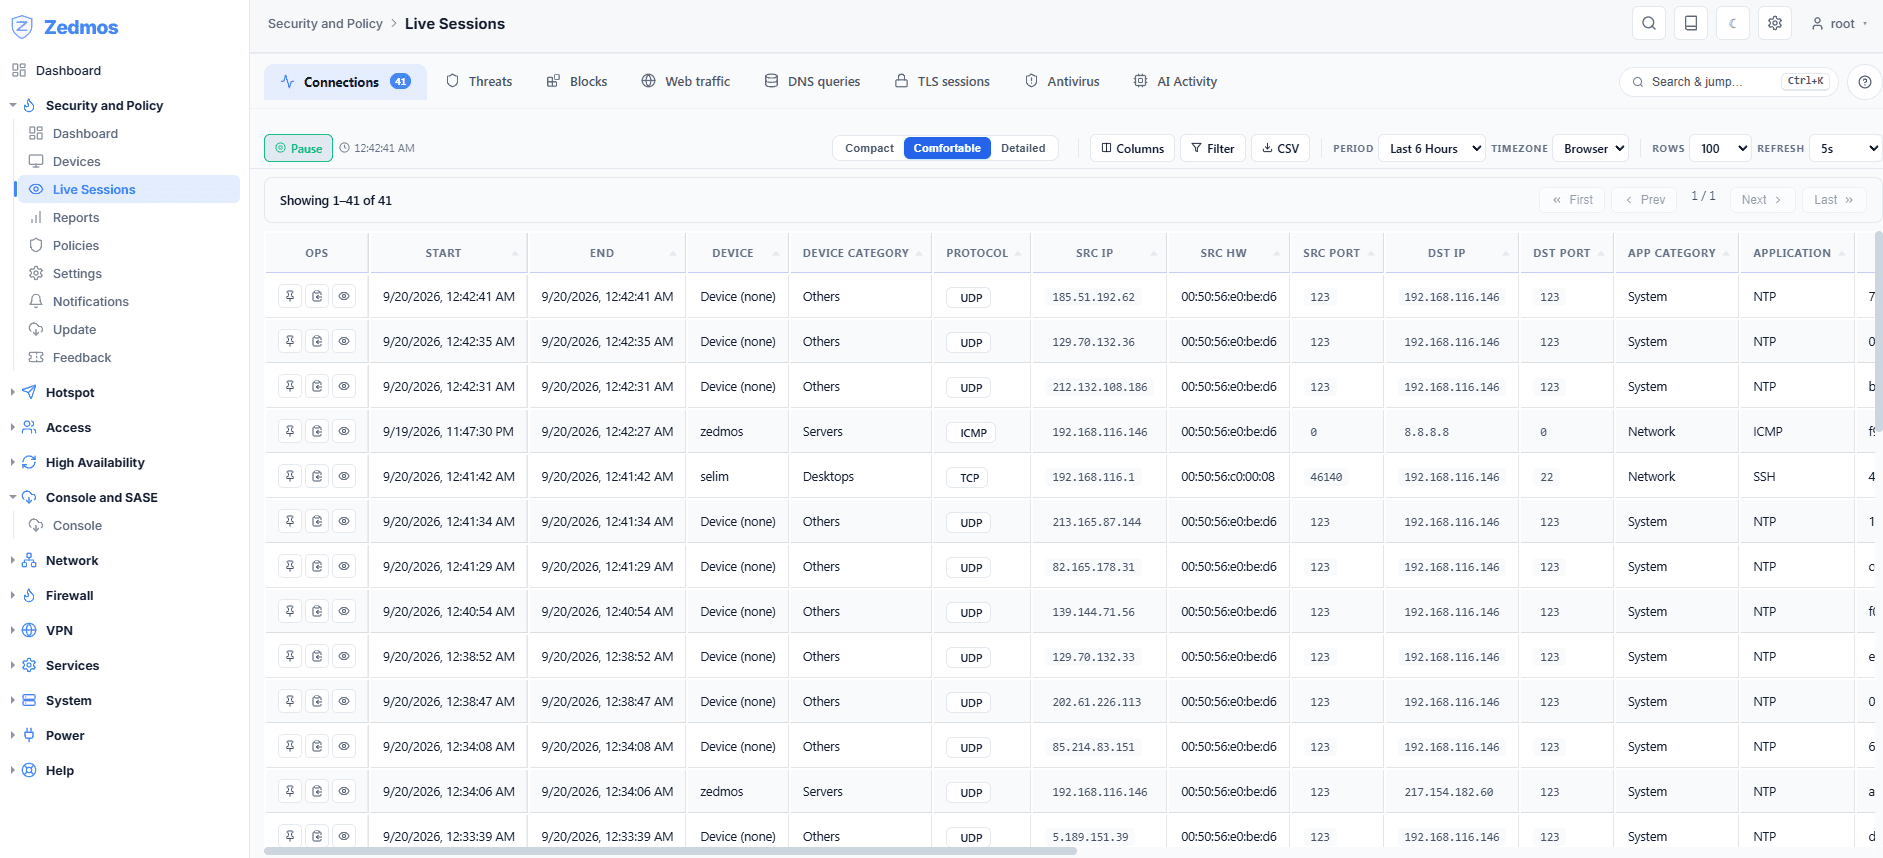
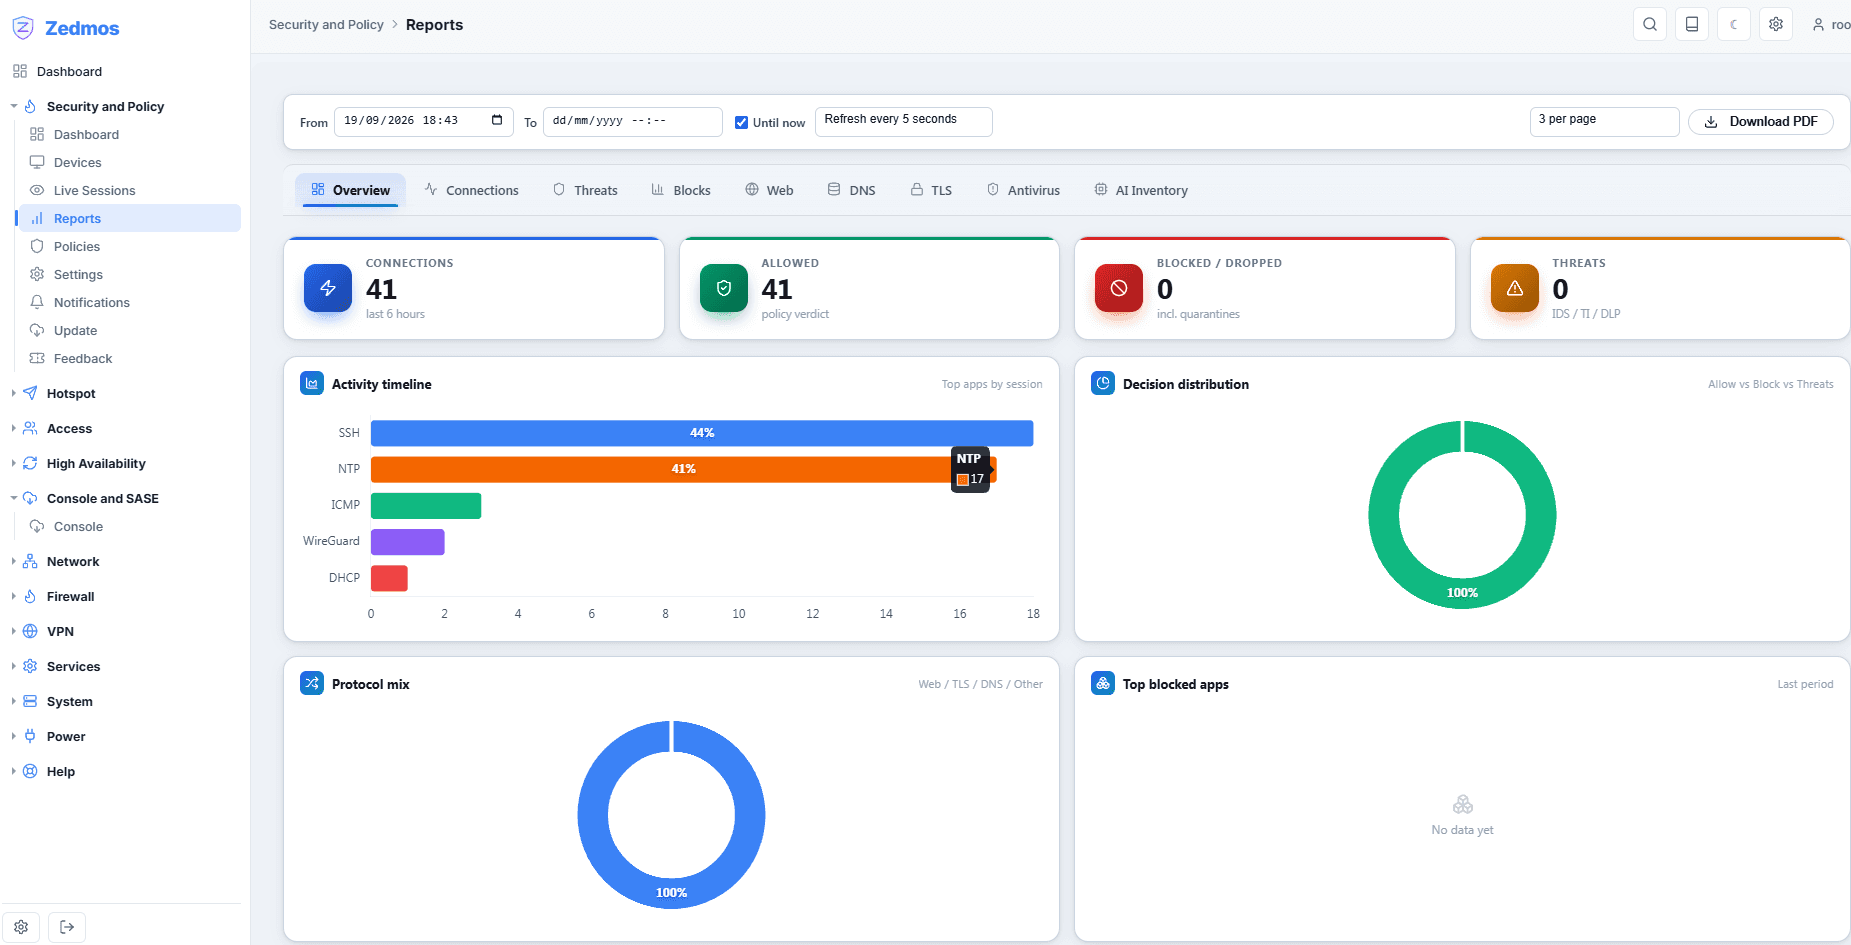
Threats, blocks and antivirus findings for the same traffic, one tab away — signatures and intelligence applied before the session was allowed to continue.
Web requests, DNS queries and TLS sessions of the same flows, each on its own tab — including what was inspected inside an encrypted connection.
Each flow carries the application the engine identified and the category it belongs to — classified by what crosses the wire, not by the port it used.
The device and its category sit on the same row as the flow, with the hardware address beside them, so a policy can name a person or a group instead of an address.
Grouped by the question each one answers. The same set on OPNsense, on pfSense and on Zedmos NGFW — one engine, one policy model, three ways to run it. Each has a fuller technical write-up under Resources.
Almost everything is HTTPS on 443, so a port-based rule can only permit or deny all of it.
Bump what you choose to; leave banking and health traffic alone by rule.
JA3, JA4 and ALPN identify the software behind a session even when it is not decrypted.
The protocol most of the web moved to, seen and controlled rather than left as a gap.
Encrypted resolution routes around a classic firewall's name-based rules. Not around this one.
Every flow on screen as it happens, carrying the decision and what drove it.
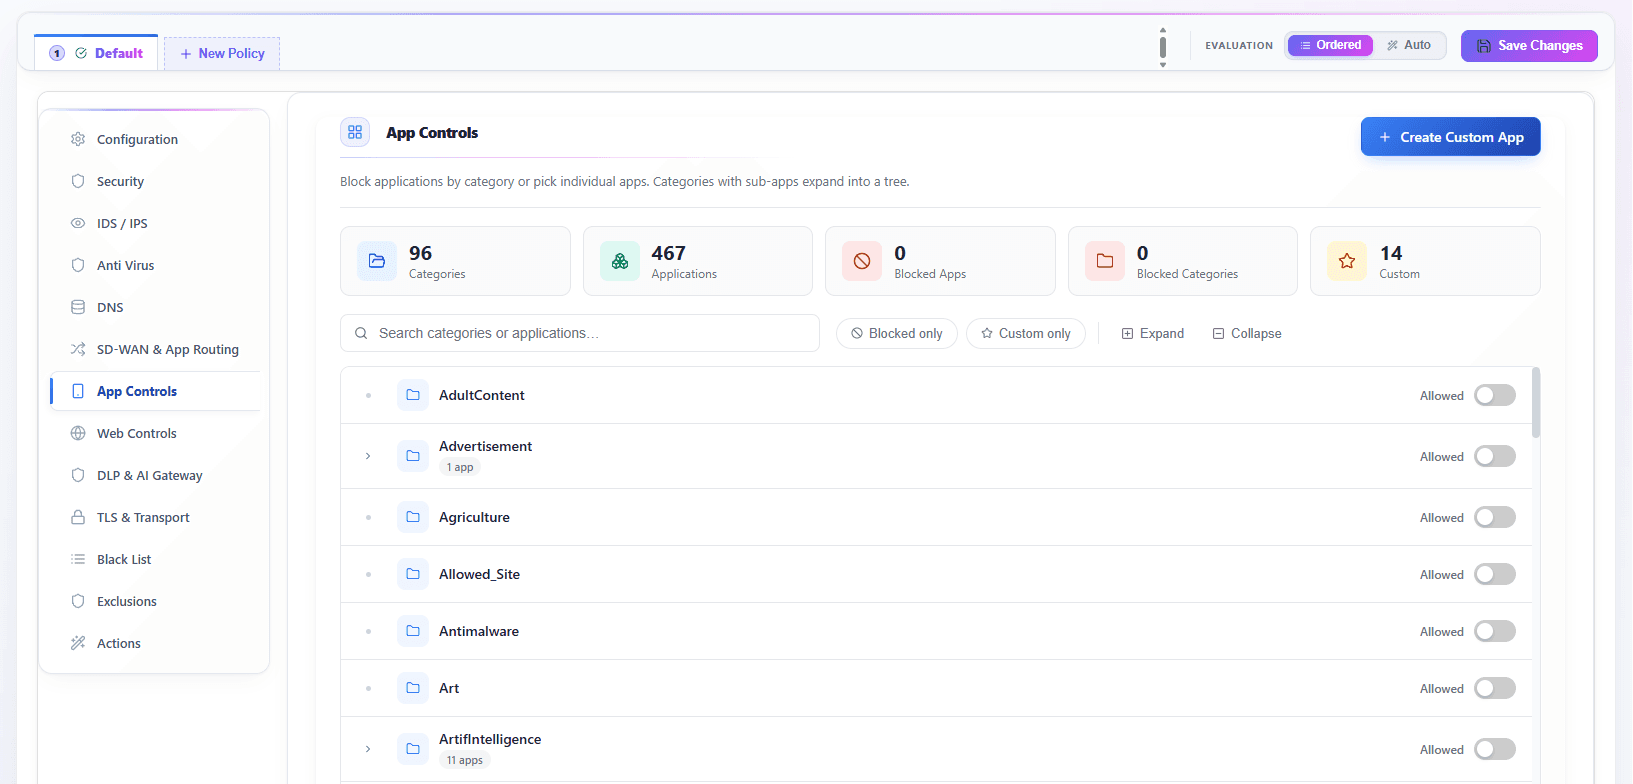
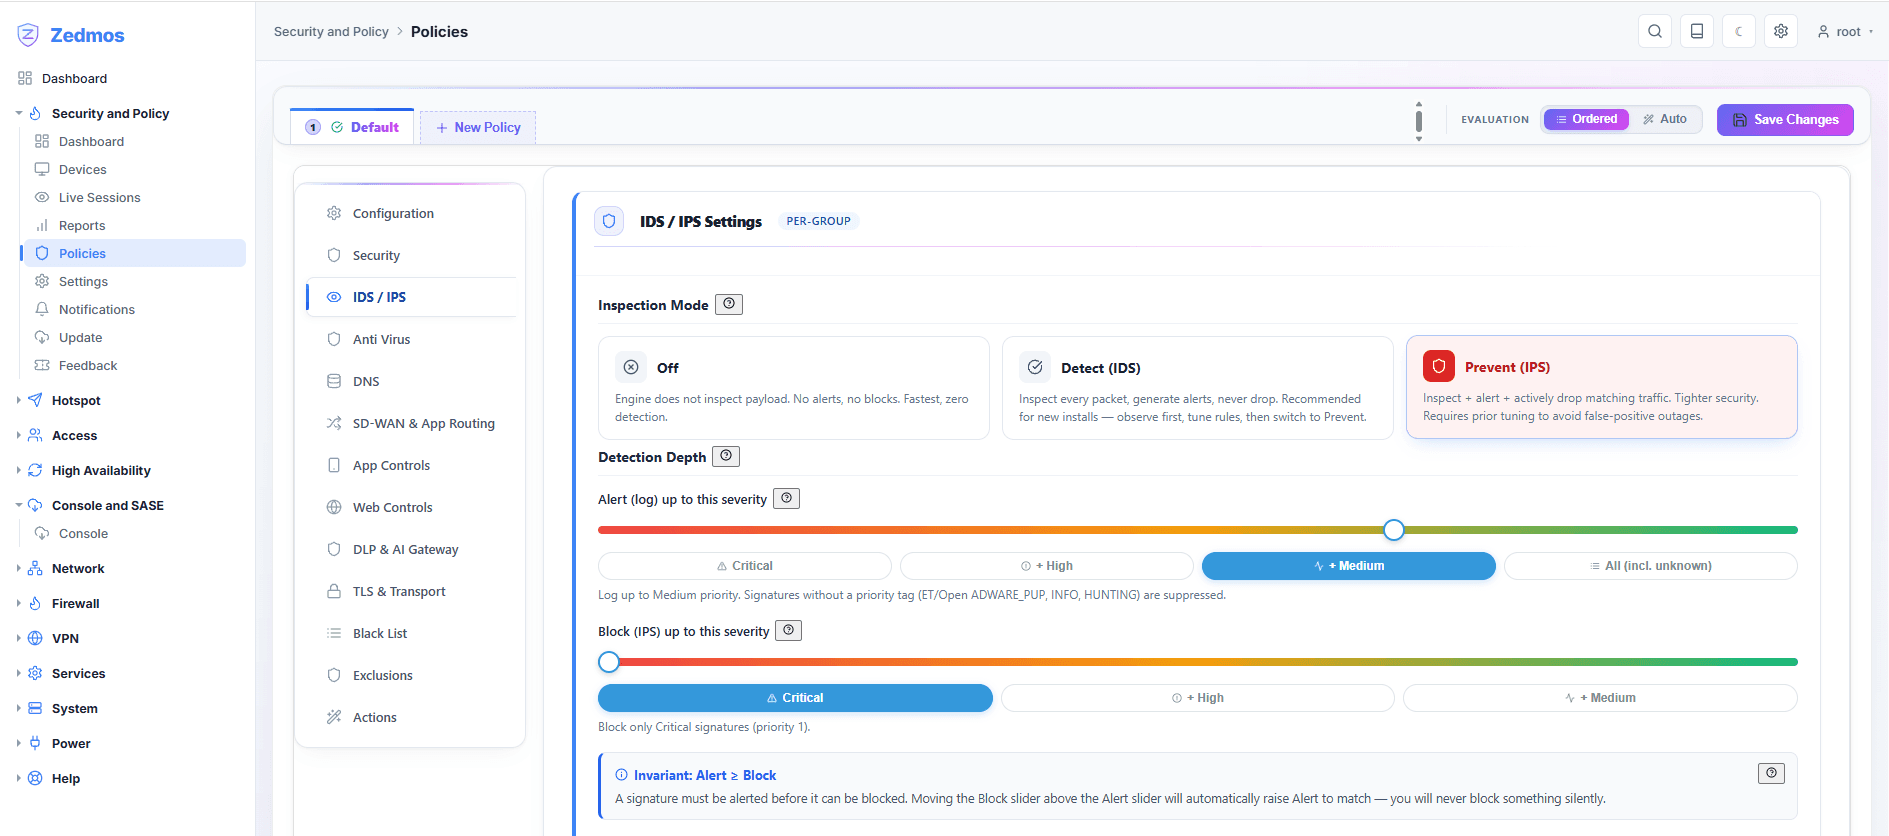
Signatures evaluated inline on the same appliance — a match is a block, not a morning alert.
Indicators gathered and cross-checked, then pushed to every firewall you manage.
Attachments and downloads examined before they land, not after.
Allow, log, rate-limit, quarantine, reset, drop — and the rest, on both platforms.
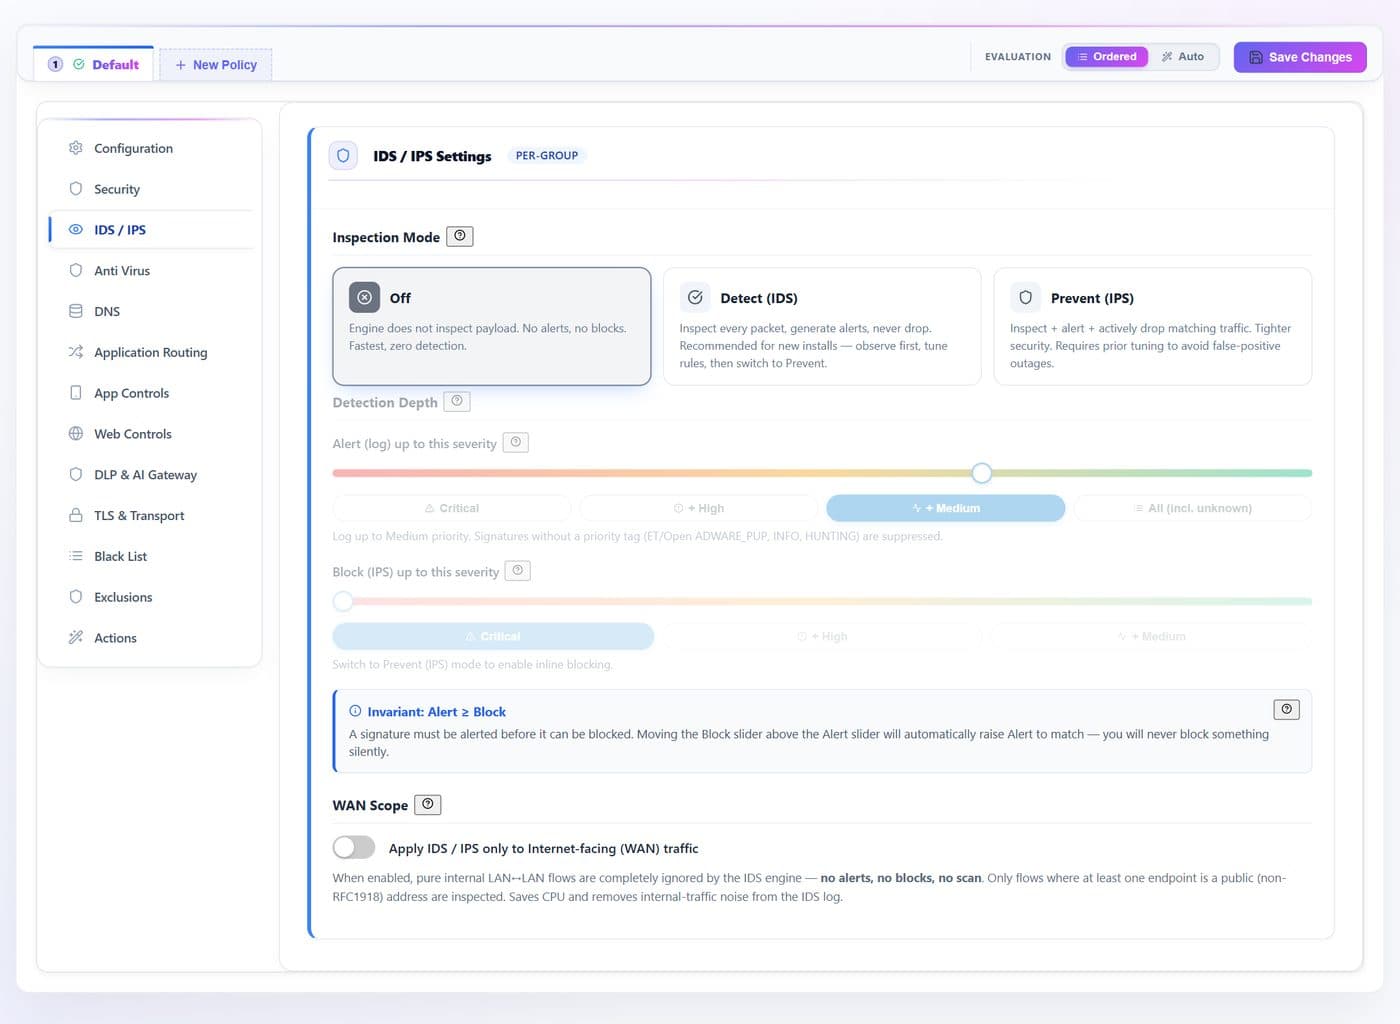
Which assistants are in use and by whom — answered without reading a single prompt.
Source code, credentials and regulated data caught on the way out, not in a breach report.
Deterministic matchers plus a local model. Sending content away to ask whether it may be sent is a contradiction.
Watch and record; strip the sensitive part and redirect; or block outright. The rule's action verb is the only change.
ChatGPT, Claude, Gemini, Copilot, Perplexity, Mistral — and an in-house endpoint you declare yourself.
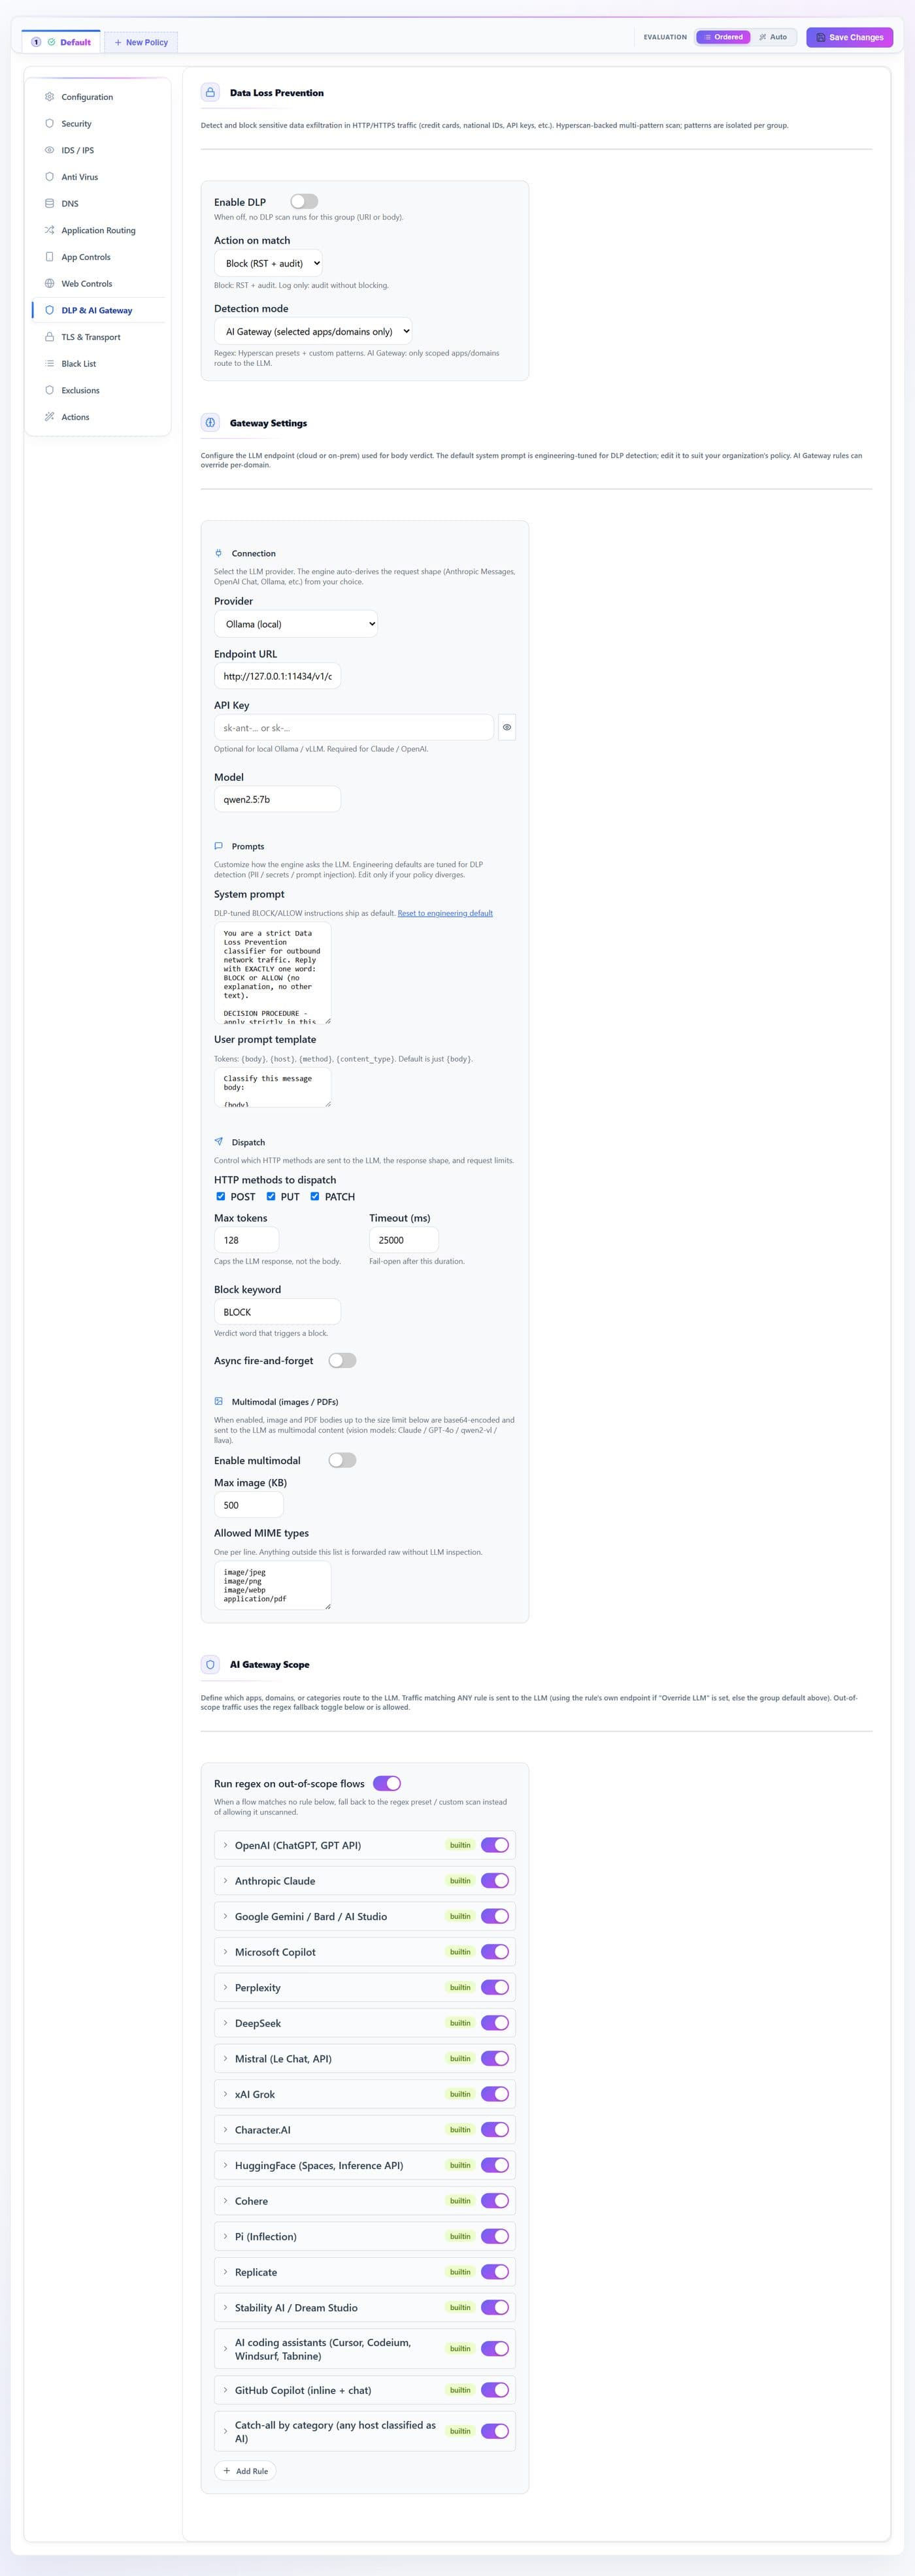
Browser, SDK or script, autonomous agent, MCP client, or none of these — every request is placed in a class before an action is chosen.
The user agent, the shape of the request envelope and the address it is posted to — a raw API endpoint and a chat surface are told apart.
A request carrying tool definitions, calls or results is what turns an assistant into something that acts. It can be allowed, recorded or refused on that ground alone.
Programmatic access to a provider nobody approved is its own case, separate from someone opening the same site in a browser.
Marking forwards the request and records it with a reason and a sensitivity class on the AI activity page — so a class can be watched for a week before anyone decides to block it.
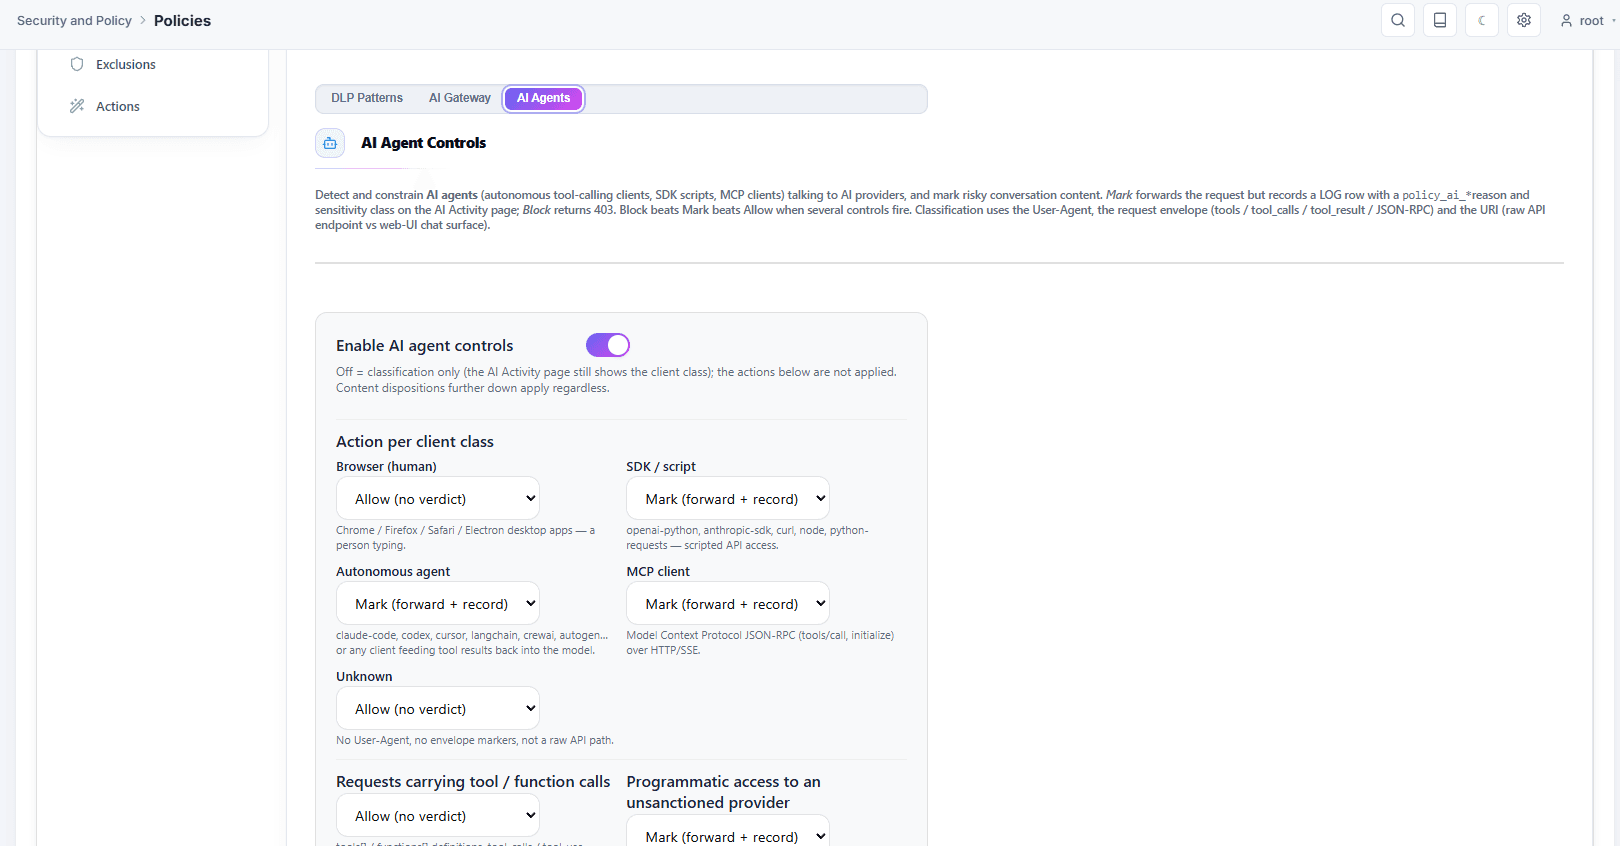
Card numbers, secrets, health and financial data, and national identity formats for twenty-two countries.
A file attached to a web form and a paragraph pasted into a chat are the same risk.
The record names the rule, what was detected and where — without keeping the content itself.
A control that lets traffic past when it cannot evaluate it is not a control on the path that matters.
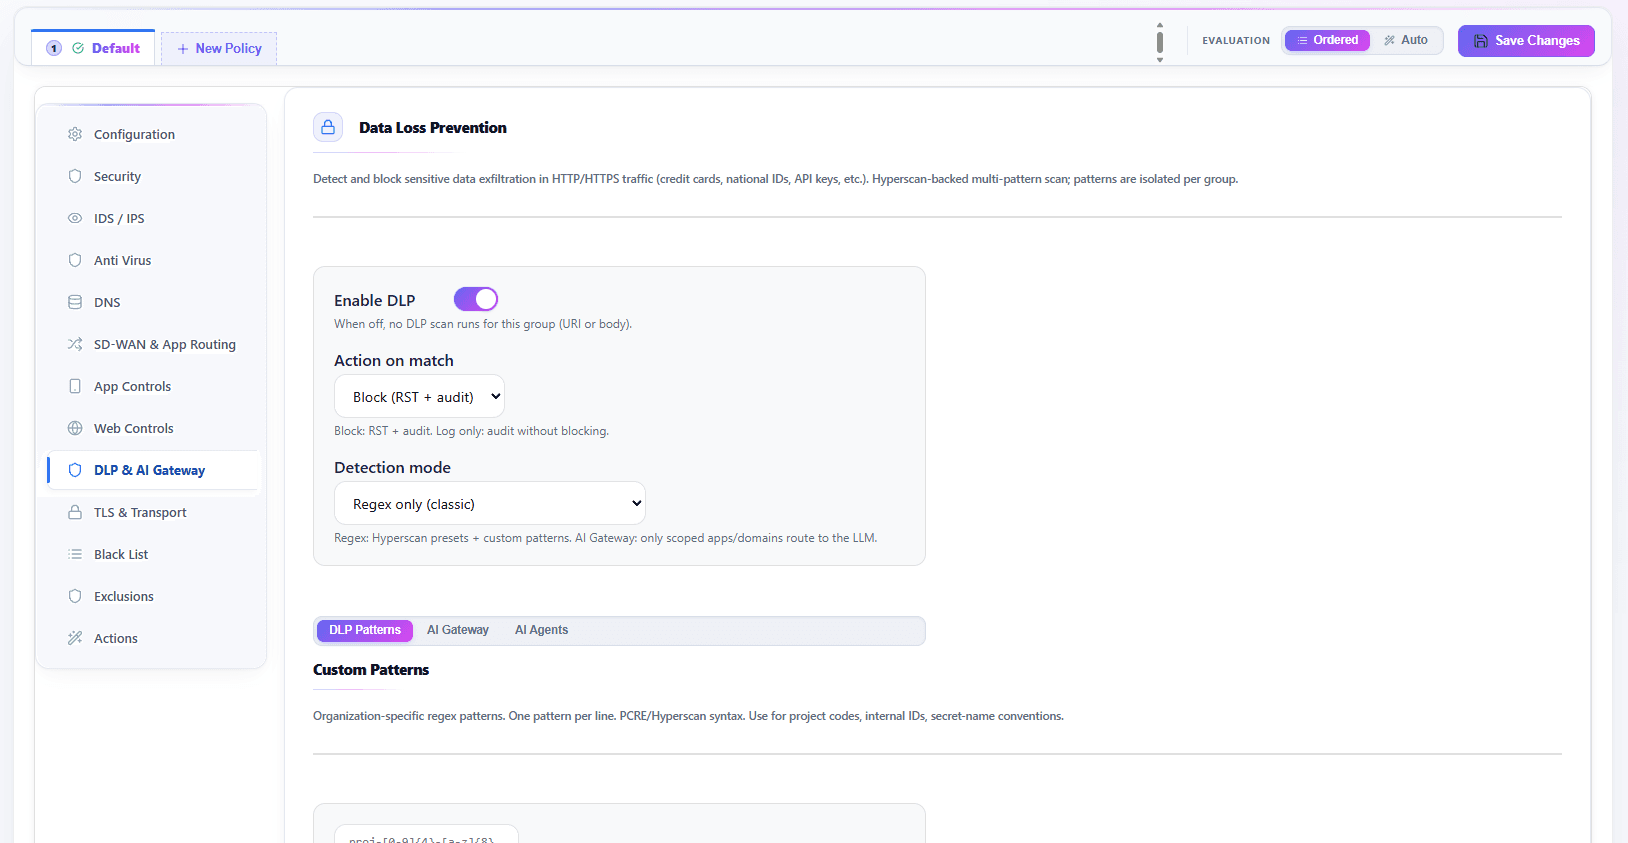
A managed laptop and a personal phone share a subnet and look identical to an address rule. For an enrolled remote device, your own Intune or CrowdStrike says whether it is healthy.
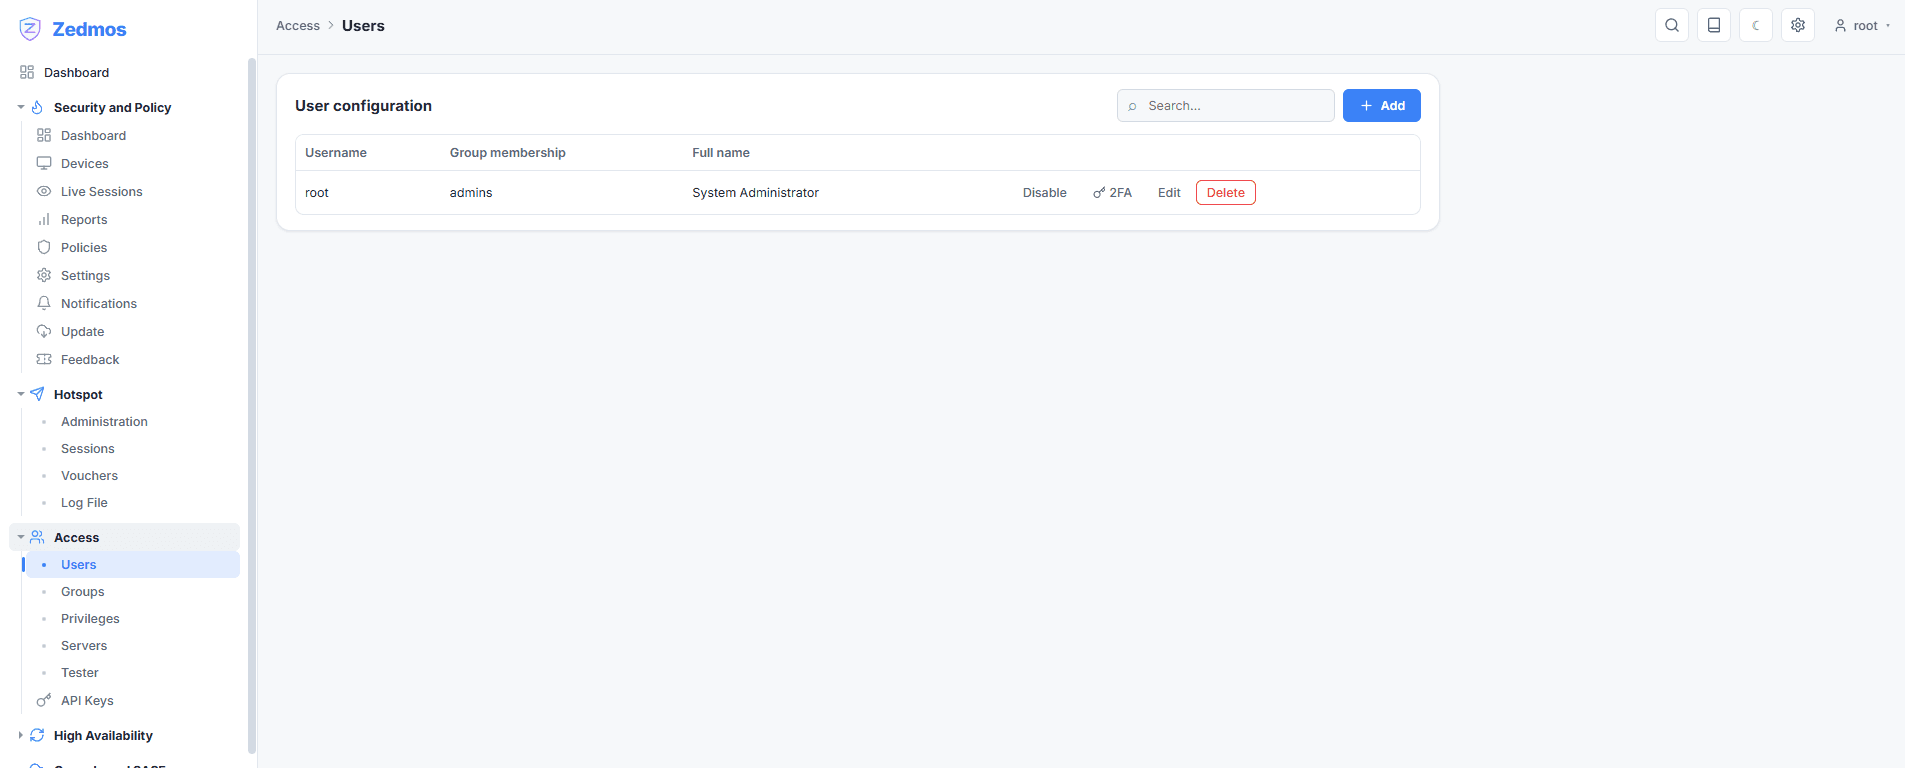
Active Directory, Entra ID or SCIM — and, for a remote person, your own OpenID Connect provider at enrolment. An entitlement follows the person, not their DHCP lease.
A device restricted to what it needs to be fixed is a device you can still fix.
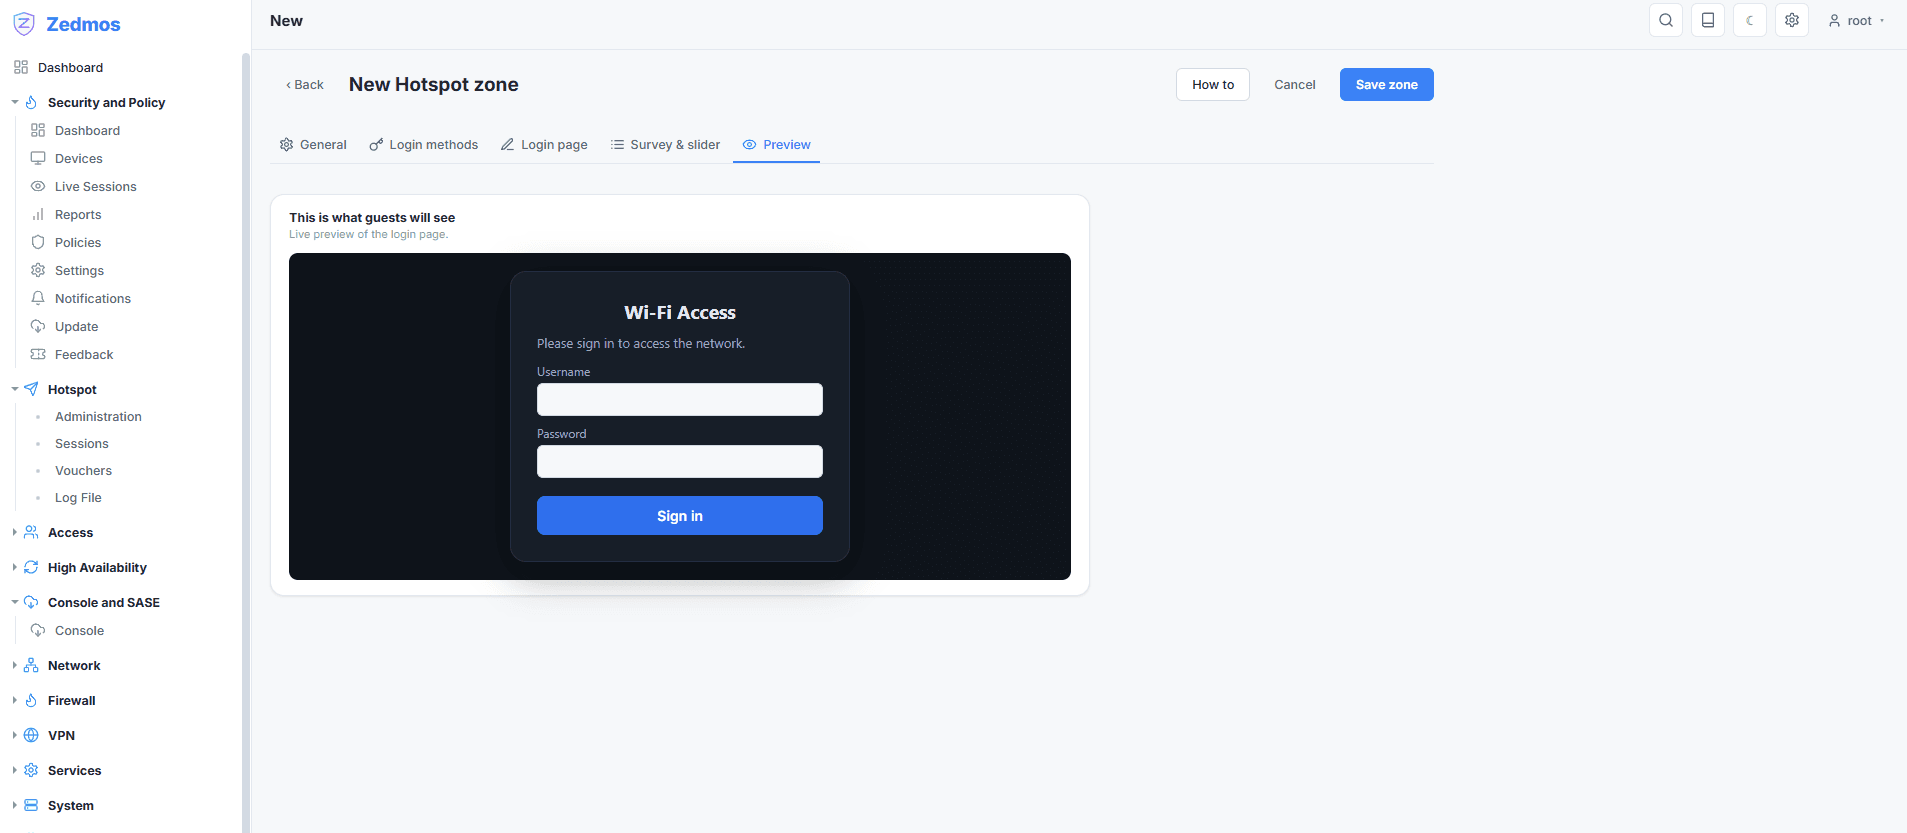
Different rules for a guest network, a server segment, and outside business hours.
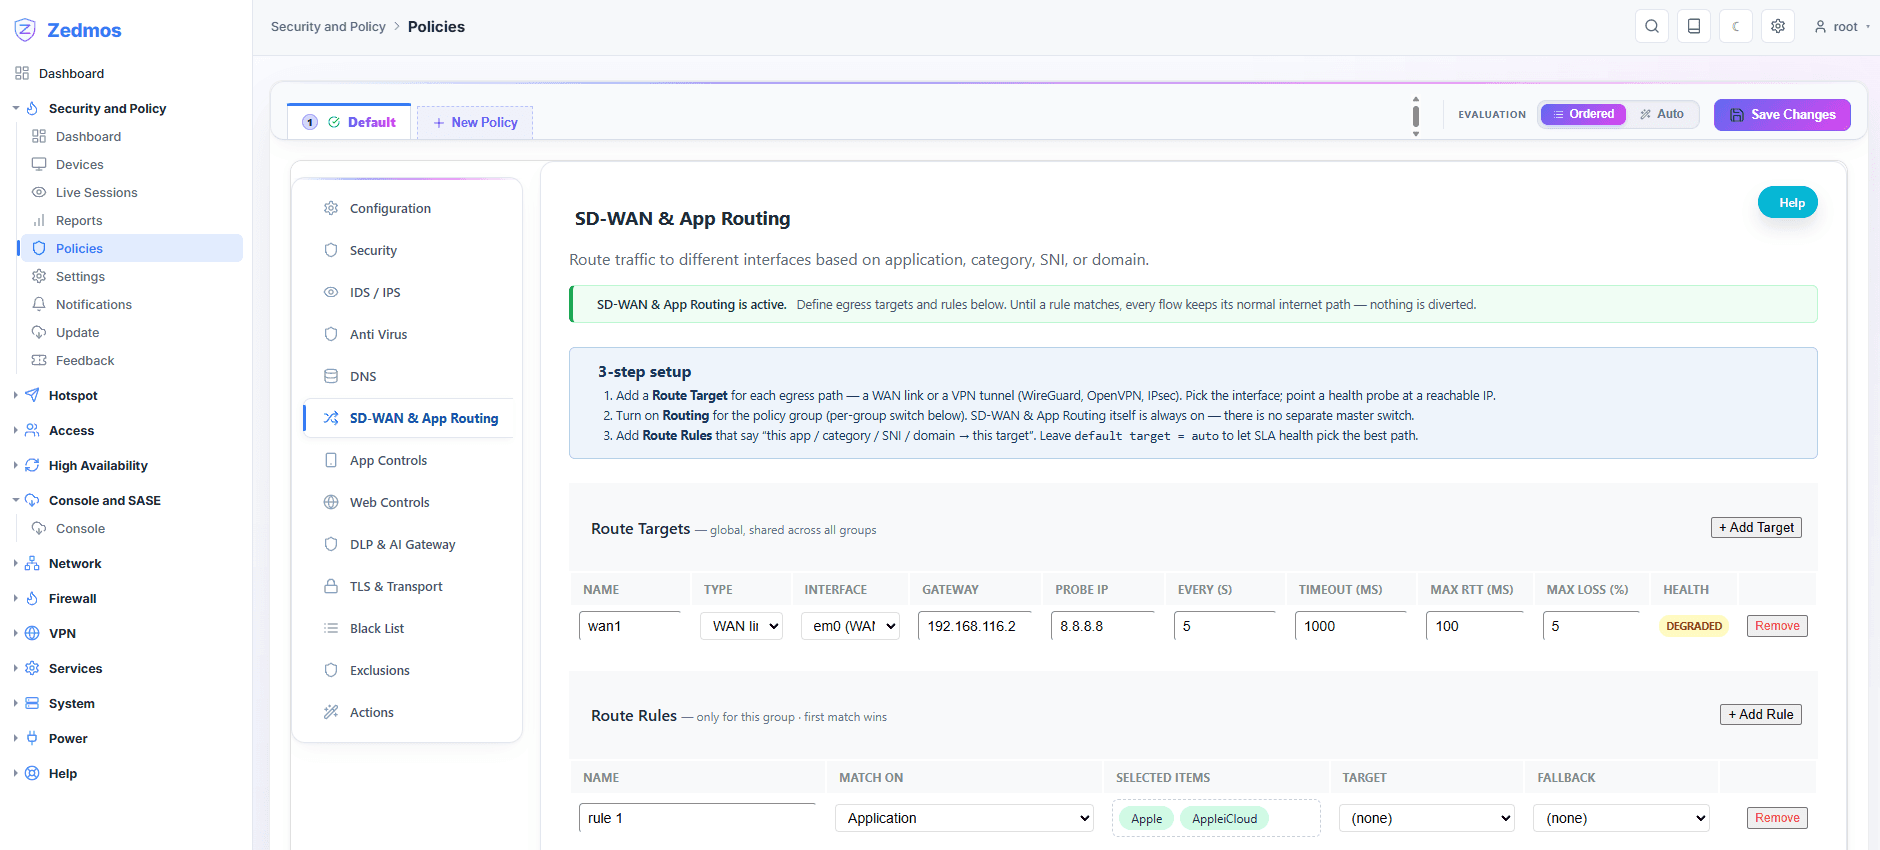
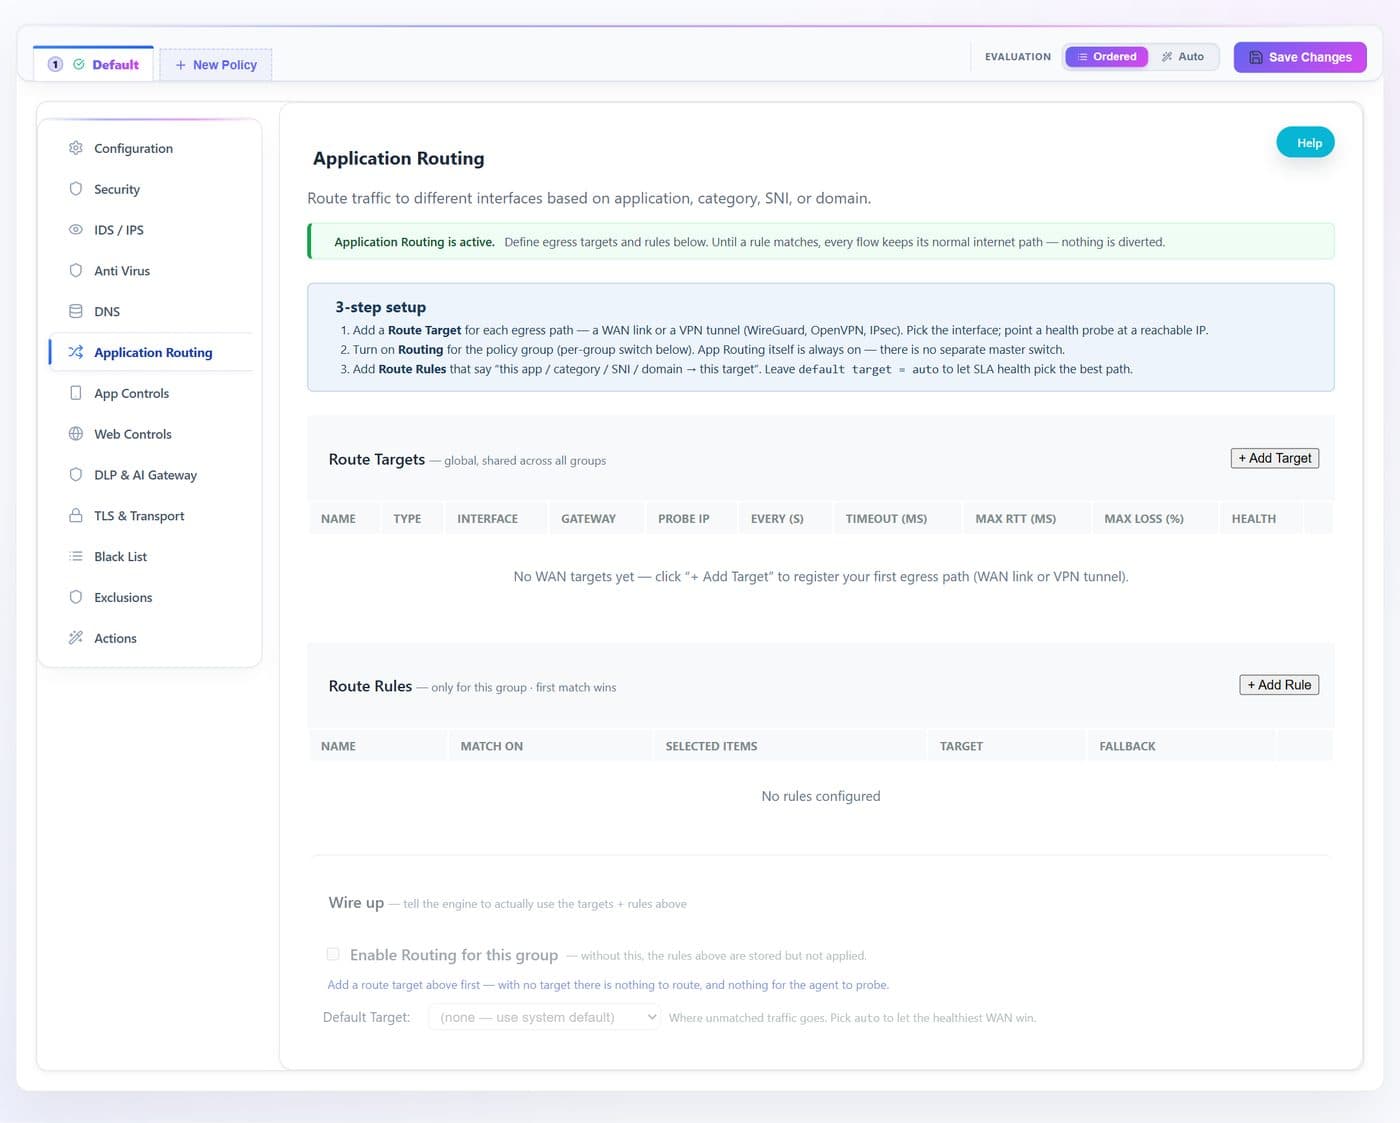
Scored on loss, latency and jitter — a link that is up and losing packets is not a healthy link.
WireGuard, OpenVPN or GRE in four shapes — one hub, a hub pair, direct tunnels between spokes, full mesh — provisioned from one topology view rather than hand-built per firewall.
A policy edit takes effect without dropping a packet or interrupting a session.
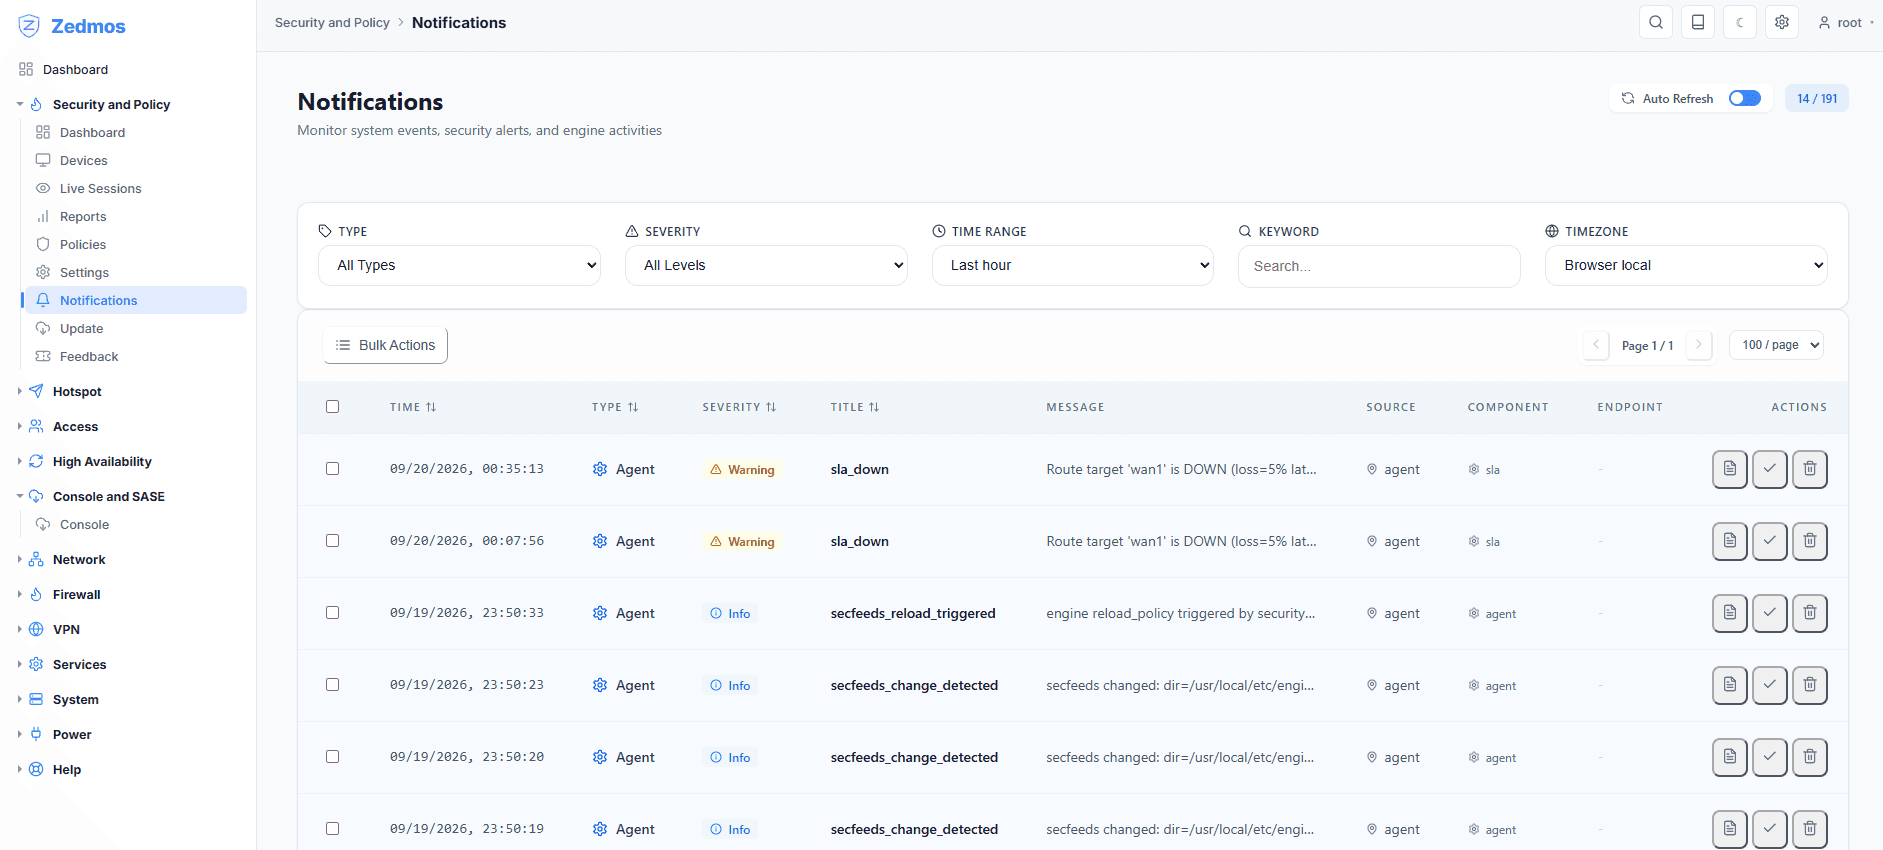
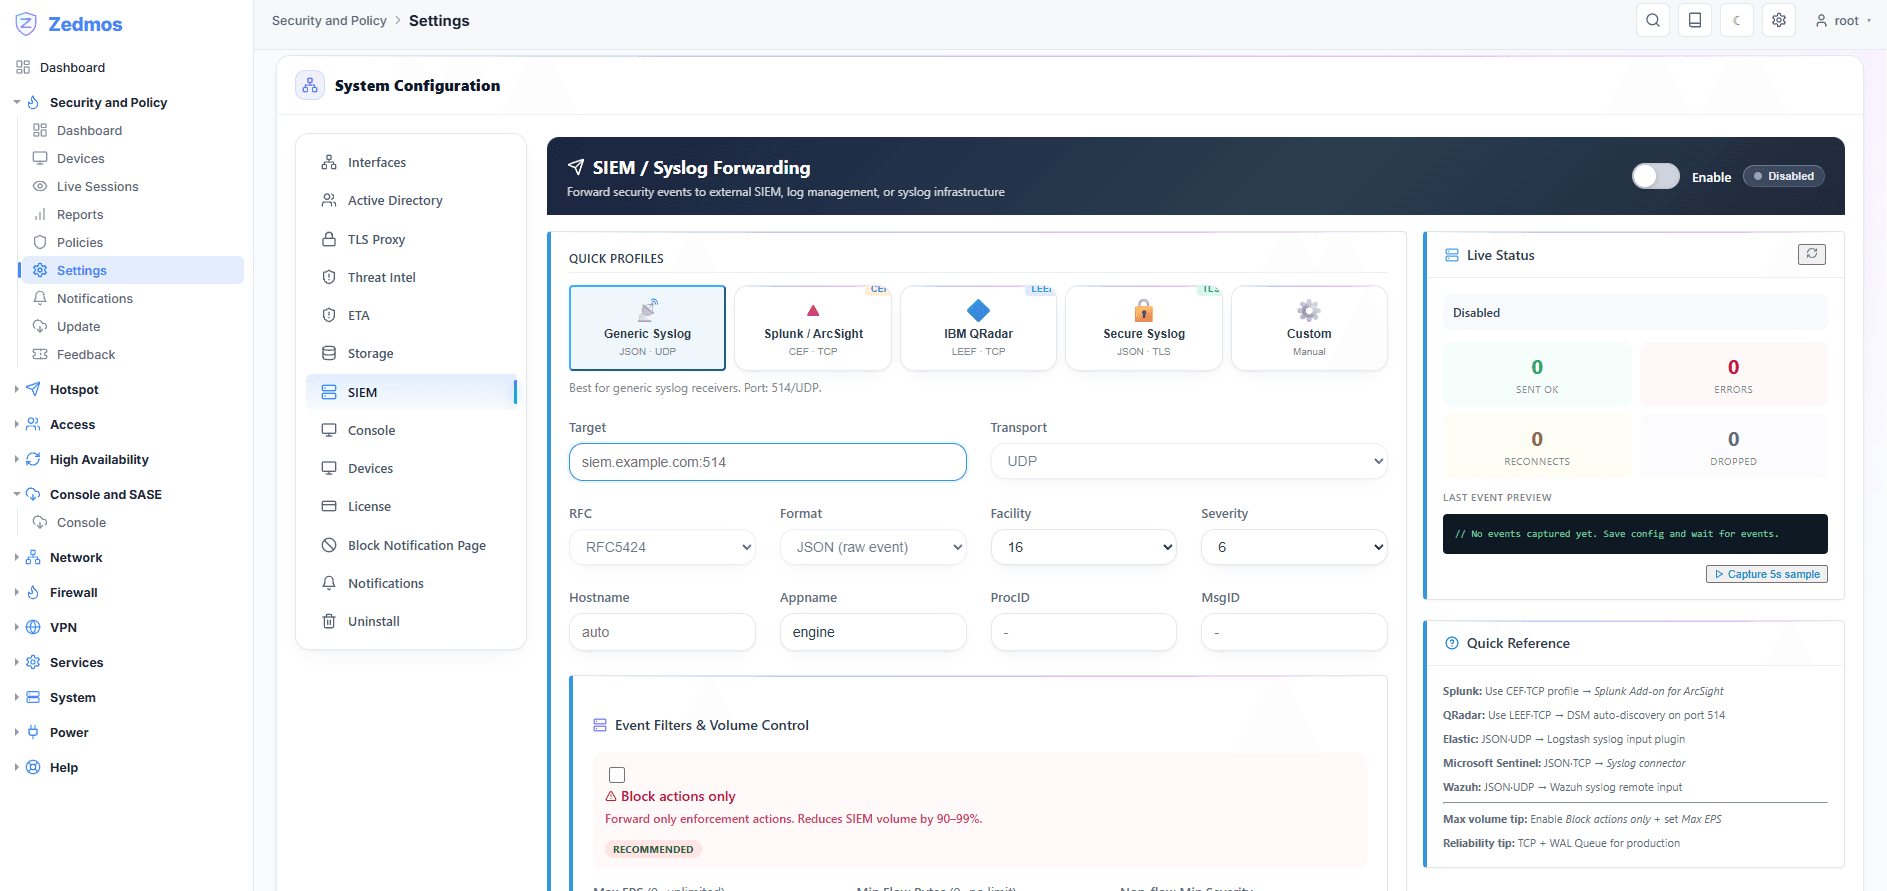
Reports and live sessions on screen, and CEF, LEEF or syslog over TLS to whatever you run.
Taken from the package repositories rather than typed into this page, so it does not drift the way a hand-written version string does.
The console and the firewall are released on their own schedules, so their numbers do not track each other. Which version each of your firewalls is running is in your console.
The appliance at a glance
Dashboard · 1 of 11
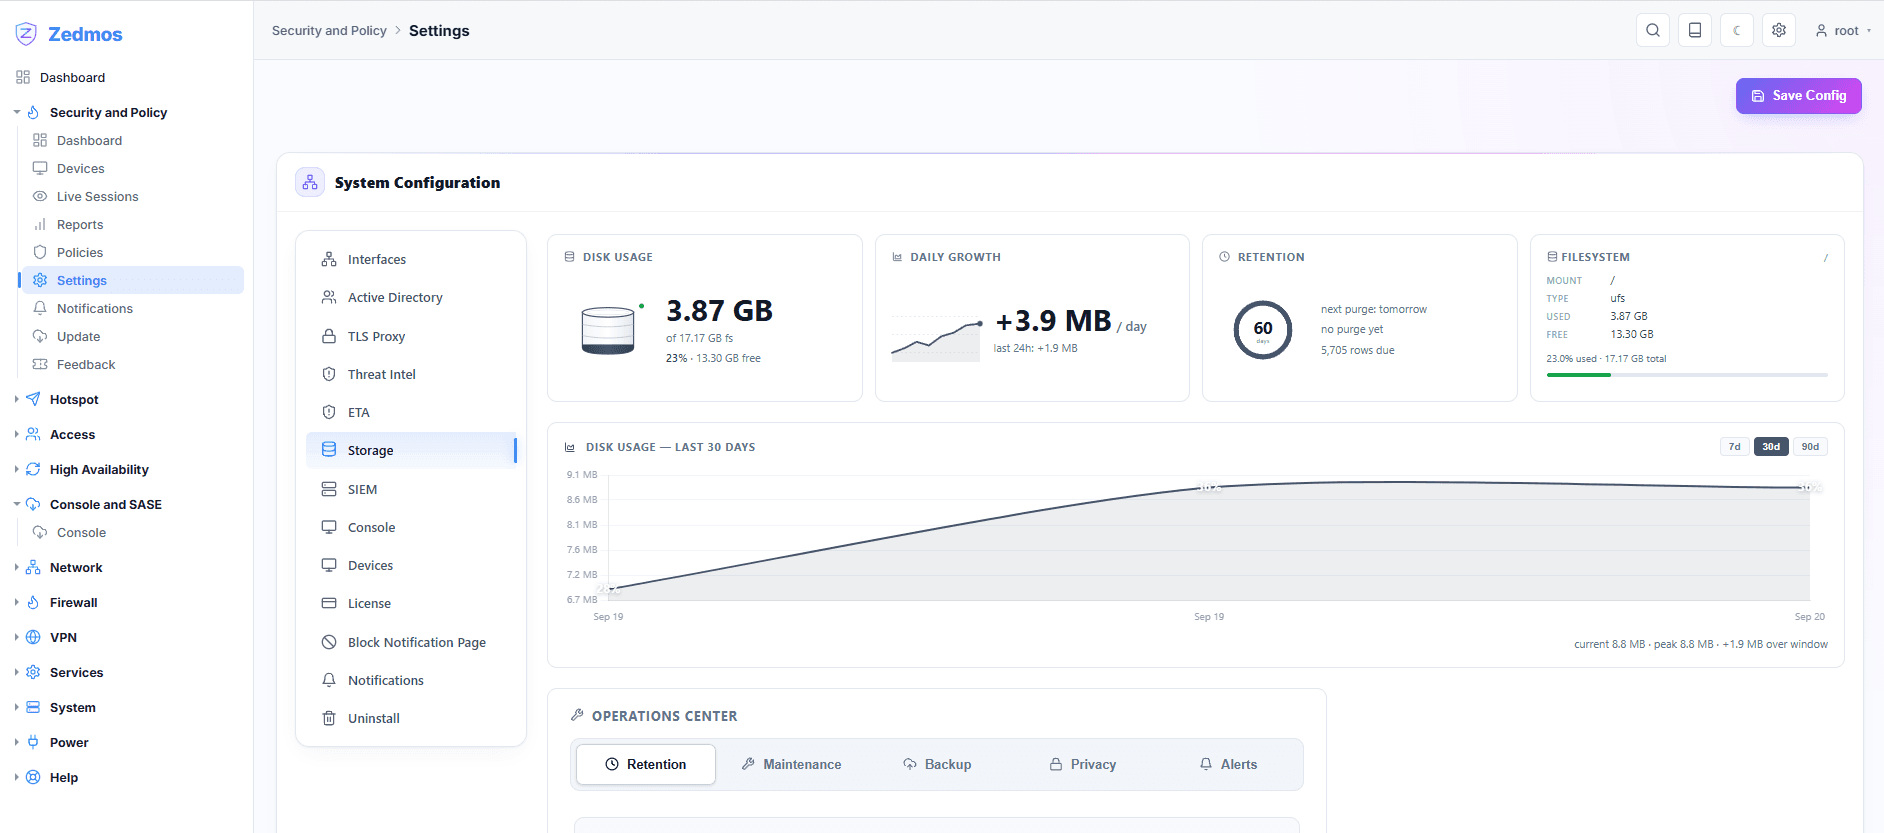
Load, memory, disk and uptime beside the state of the engine services and the cloud link, with live throughput, a per-interface traffic graph and the top applications, remote hosts and devices.
Traffic is classified, inspected and decided on the same appliance that routes it. No packet, no payload and no session record is sent to Zedmos.
Applications, categories, domains, users, groups, devices and zones select traffic; sixteen actions decide what happens to it. The same model on both platforms.
TLS inspection with fingerprinting and selective bumping, plus visibility and control over QUIC, DNS-over-TLS and DNS-over-HTTPS.
Four exams with published objectives, a pass mark and a credential that can be verified by anyone holding the number. A partner or an appliance maker can staff a practice on this rather than on one person’s familiarity.
ZCA-101
Fundamentals: what the engine does, where it sits in the network, and the vocabulary the rest of the ladder assumes. Self-paced, and the entry point to every other credential.
60 · 90 min · 70% to pass · 24 months valid
ZCP-201
The working certification: install it, place it correctly, write policy that does what you meant, read the reports, and keep it updated. Assumes hands-on time with a real appliance.
80 · 120 min · 75% to pass · 24 months valid
ZCS-SASE-301
Multi-site and remote access: overlay design, hub selection, failover behaviour, per-user enrolment and the routing decisions that follow. Assumes ZCP and a working multi-site estate.
60 · 90 min · 78% to pass · 24 months valid
ZCS-MSP-302
Running many customers from one console: tenancy and access scoping, enrolment at scale, policy templates and the drift they produce, entitlement and billing, and keeping one customer's incident inside one customer's estate. Assumes ZCP and a live multi-tenant deployment.
60 · 90 min · 78% to pass · 24 months valid
One page per incumbent, built from that vendor’s own documents and public records — licensing, lifecycle, management, jurisdiction and exploit history, each row with its source.
This page makes the argument. These say how it is actually done, screen by screen and setting by setting.
The inspection pipeline itself: the fast path, classification, policy evaluation and the transmit layer.
Every capability with its own page: how it works, what is under it, and what it is measured at.
From a bare appliance to a running engine, step by step.
A complete next-generation firewall: ZedmOS, a FreeBSD-based operating system, the Zedmos inline inspection engine attached directly to the interfaces, and a policy model that decides once per session. It is installed from an image onto x86 hardware you choose.
No. Traffic is classified, inspected and decided on the appliance that routes it. No packet, payload or session record is sent to Zedmos. The console distributes policy and collects records; it is not in the packet path.
Classification across more than 200 protocols, intrusion detection and prevention reading the Suricata rules format, TLS inspection with JA3/JA4 fingerprinting and selective decryption, control over QUIC, DNS-over-TLS and DNS-over-HTTPS, data loss prevention with 69 detectors, an AI gateway, per-application routing across uplinks, and WireGuard, OpenVPN and GRE overlays. One policy model with 16 actions and 26 threat categories.
Per firewall, with no hardware in the licence. Three tiers: Free (three firewalls for thirty days), Team (per firewall) and MSP (multi-tenant, unlimited firewalls, billed monthly in arrears). Prices are quoted on request. A lapsed licence makes the console read-only and never stops the firewall.
Zedmos is software on hardware you own rather than an appliance with a subscription bundle; management is self-hosted or hosted in Frankfurt rather than in a vendor cloud; the vendor is German and answers under EU law; and the exploit record is published: zero entries in the CISA Known Exploited Vulnerabilities catalogue. The comparison pages set each vendor's own documents beside Zedmos, with a source for every row.
Yes. The same engine installs as a package on an OPNsense or pfSense CE box you already run. Existing rules, interfaces, NAT and VPNs are untouched, and it uninstalls from the settings page in one step.
Demo & pricing: info@zedmos.com
Request a demo